Compliance you can show, not just claim
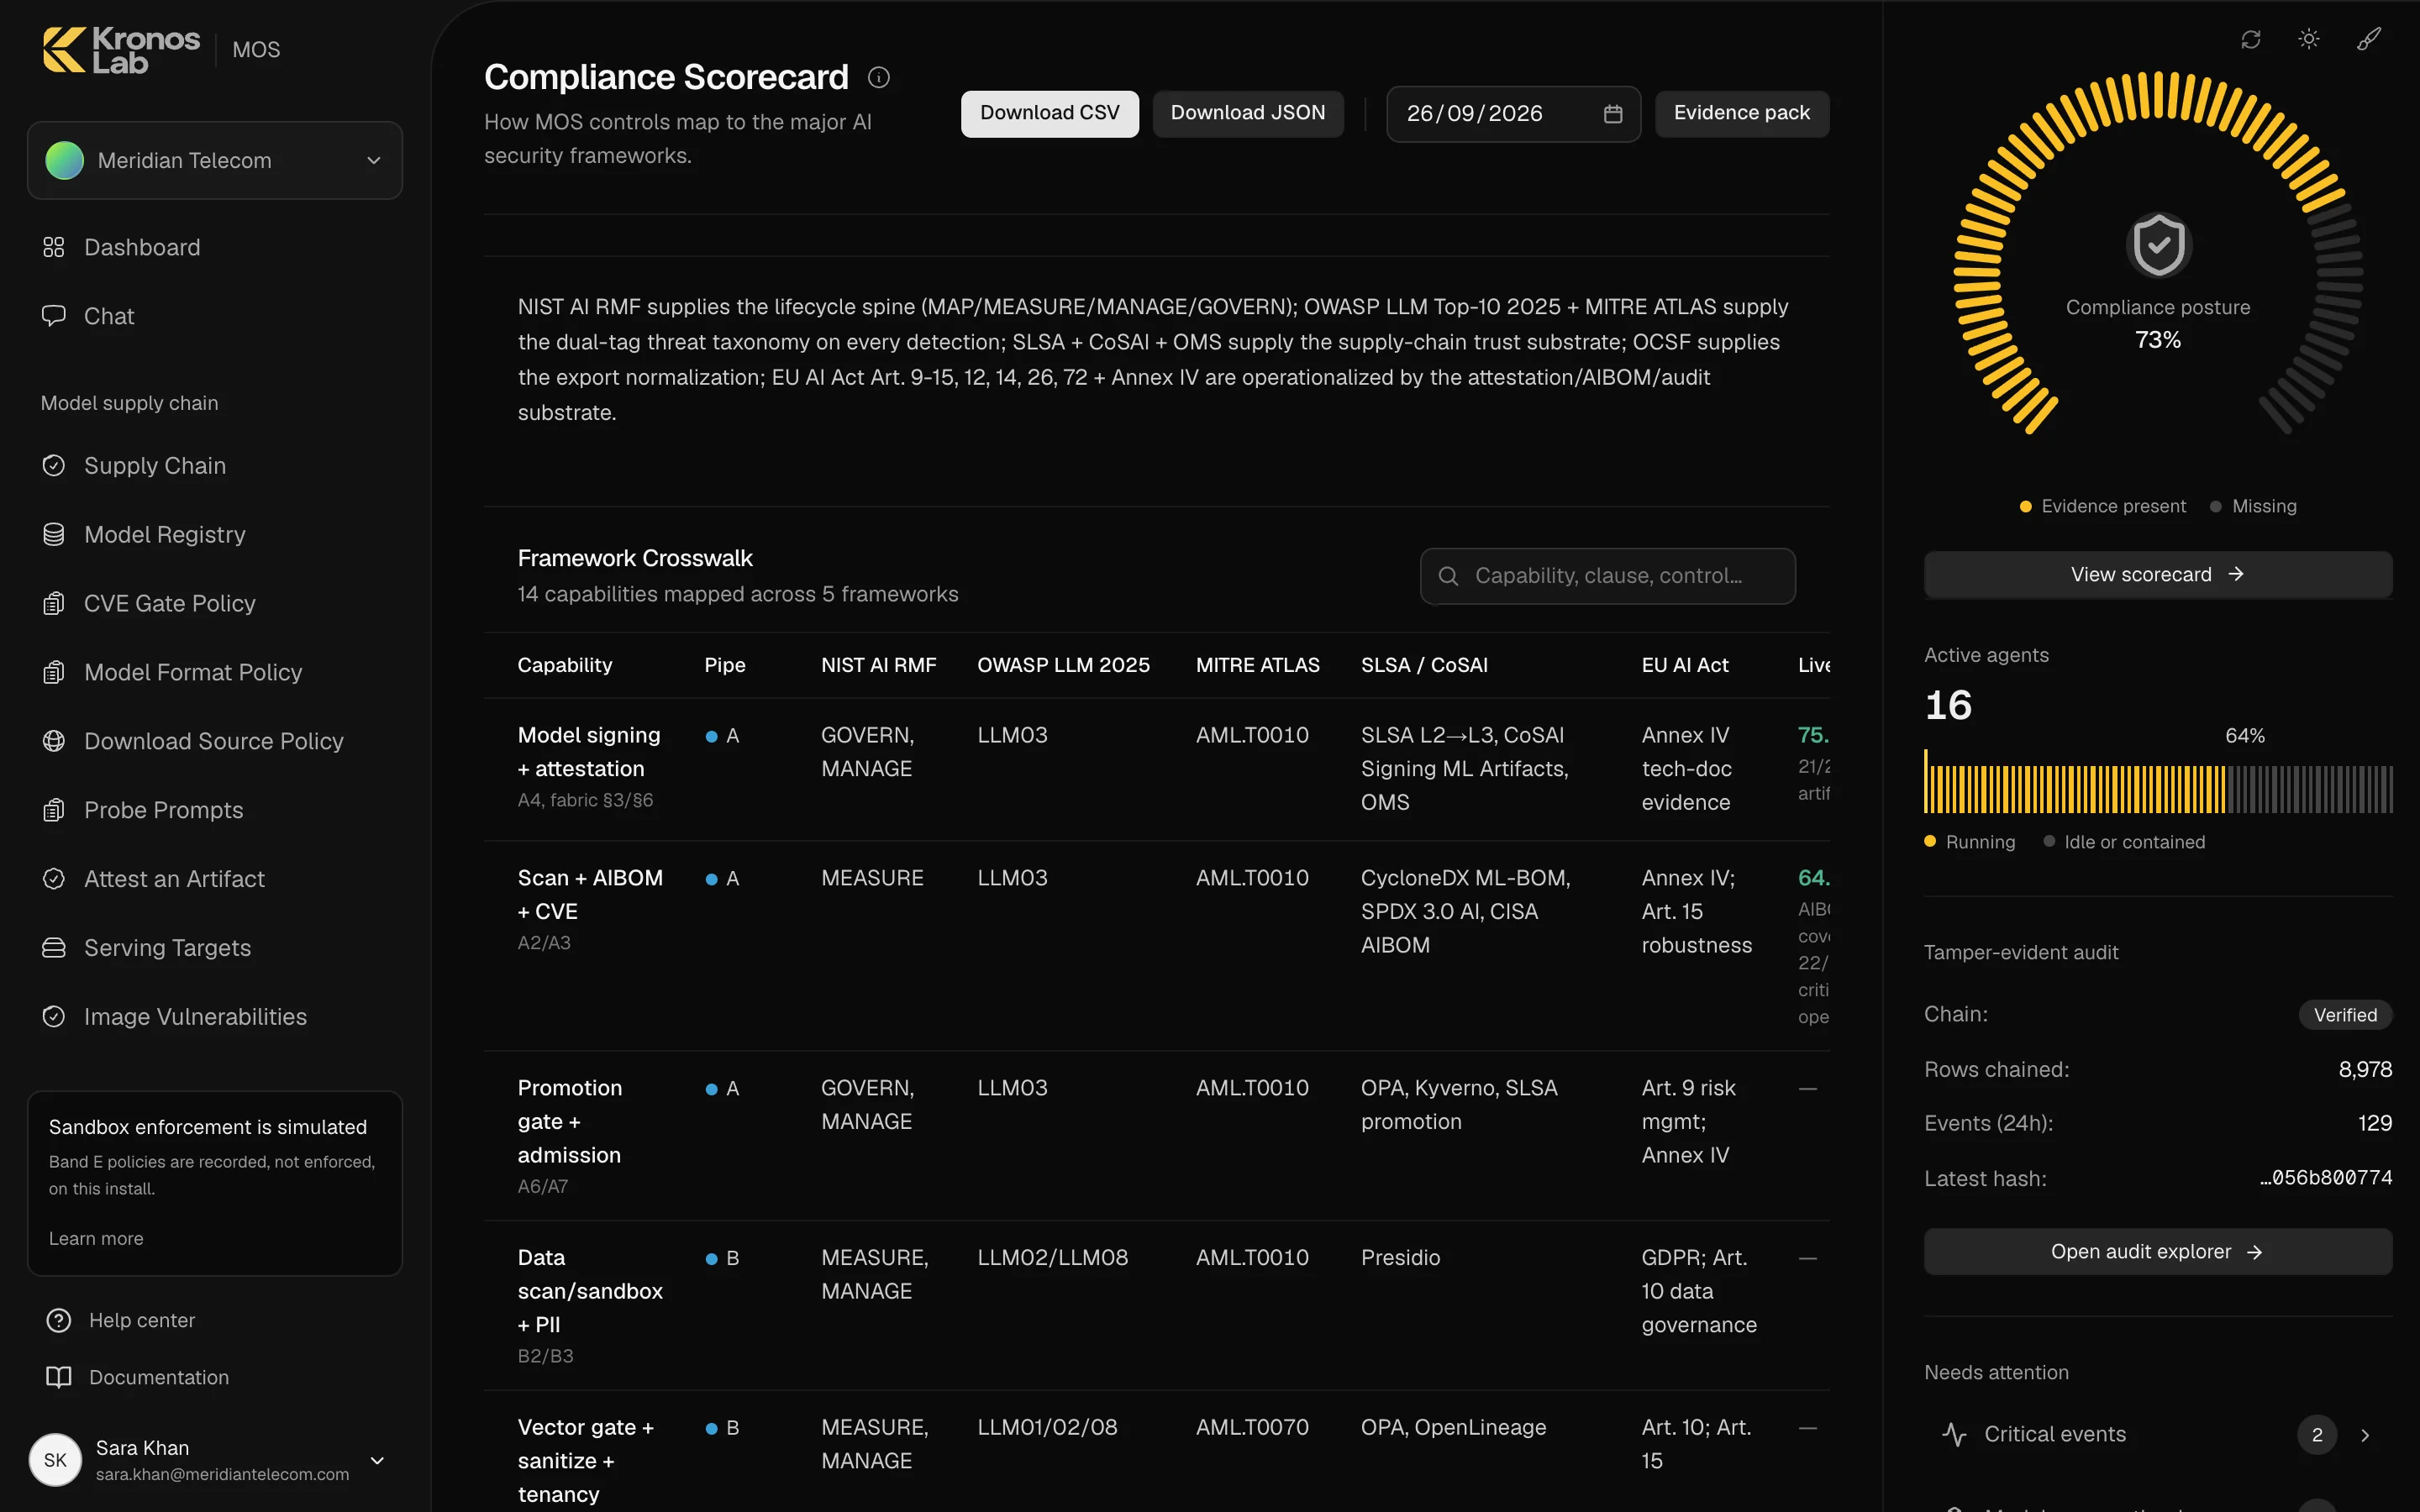
Kronos Lab was built against the known AI security frameworks first. Every control across the AI factory, from model intake to agent runtime, maps to the clauses you answer to and leaves the record that proves it held.
Four places to start
Pick the framework you are audited against, or start with the evidence.
OWASP Top 10 for LLMs and agents
Every risk on both OWASP lists, how it shows up across an AI factory, the control that answers it and the evidence it leaves.
International standards
ISO/IEC 42001, 27001 and 23894, NIST AI RMF and its Generative AI Profile, the EU AI Act, CIS Controls and the OECD principles.
Middle East and North Africa
Saudi Arabia, the UAE, Qatar, Oman, Bahrain and Egypt: which instruments bind, which guide, and what each asks of AI.
Audit evidence
What the decision record holds, how it is kept, and the artifacts you hand an auditor, mapped to the clauses they test.
How the mapping works
Compliance here is a by-product of running the gates, not a separate exercise.
- 1
A control runs
A gate in one of the four bands checks a model, a dataset, a prompt or an agent action against policy.
- 2
It decides and says why
Allow, hold or block, with a reason code, the policy version and the identity of what was checked.
- 3
The decision is recorded
The record is appended to a hash-chained log and forwarded to your SIEM within seconds.
- 4
The record maps to a clause
Each control is mapped to the clauses it satisfies, so the evidence for an audit already exists when the auditor asks.
Kronos Lab supplies controls and evidence for your compliance programme. It does not certify you: certification and legal conformity remain with your organisation and its assessors. Framework details on these pages were reviewed in October 2026.