Data
Data ingestion and encrypted retrieval
Retrieval is an attack surface, and an embedding is not anonymous: source content can be rebuilt from it. Only clean, de-identified, signed content reaches the store, and it arrives already encrypted under keys you hold.
- Ingest
RAG documents, notebooks, runtime uploads
Files, structured data and notebook uploads arrive through the platform. Every object is tagged with its tenant, source and uploader before anything else happens.
Ingestintake.doc src=rag-upload files=64 types=pdf,docx,ipynb bytes=1.2G
- Malware and sandbox
Detonate, then quarantine
Anything active, such as macros, embedded scripts or notebook cells, runs in a sandbox first. Infected objects are quarantined, not dropped, so the SOC can review them.
Malware and sandboxscan.malware sandbox=on detonated=6 quarantined=1 1 BLOCKED
- PII detection
Presidio finds it before the index does
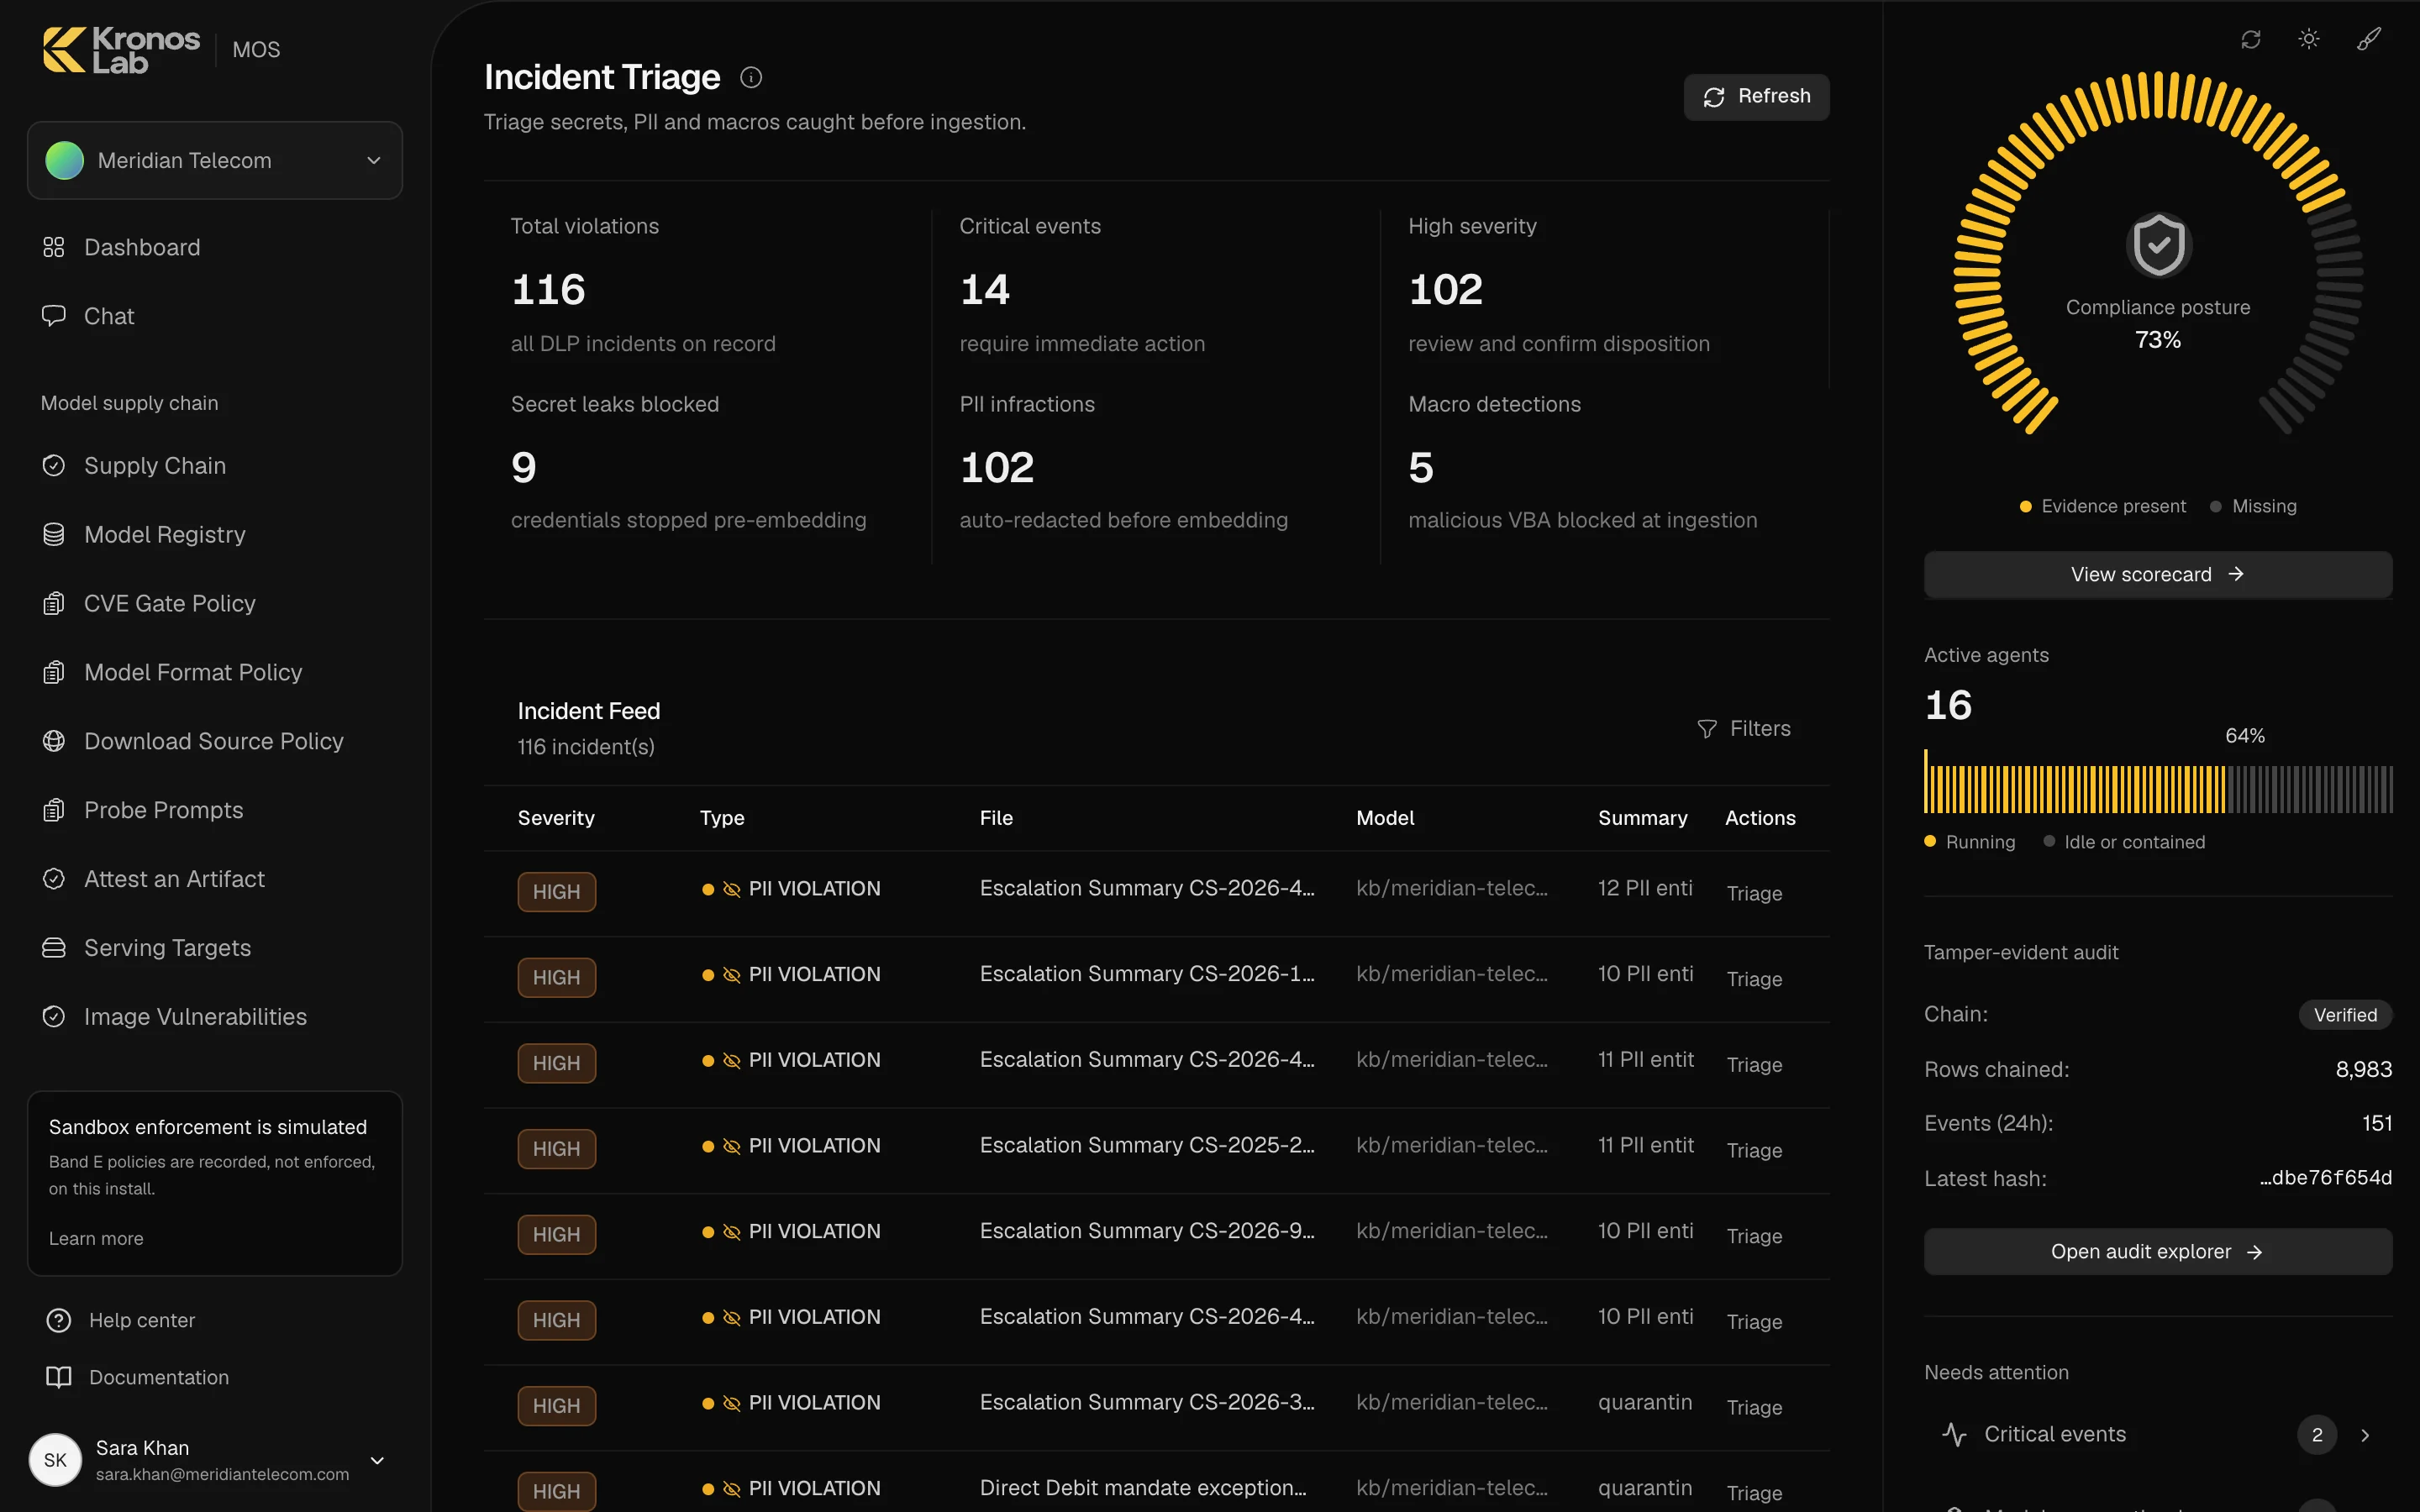
Entity detection finds identity numbers, contact details and names. A per-tenant policy chooses to redact, mask or reject. This is where residency and privacy obligations are enforced.
PII detectionscan.pii engine=presidio NATIONAL_ID:12 PHONE:31 NAME:180 action=REDACT
- Data signing
Provenance for every chunk
The cleaned corpus is hashed and signed, so a retrieved answer traces back to an approved document version. That is the difference between a citation and a guess.
Data signingsign.dataset manifest=sha256:41ab…9c02 chunks=48,912 provenance=recorded
- Encrypt with your keys
Encrypted before it becomes an embedding
Content is encrypted the moment it turns into AI data, under a key in your own HSM or KMS. The platform never holds key material, so a breach of the platform is not a breach of the content.
Encrypt with your keysencrypt.embed kms=customer-hsm key=cmk/kb_prod platform_key_access=none
- Vector gate
OPA guards the write path
Nothing writes to the index directly. An OPA policy checks that the batch is scanned, PII-clean, signed and encrypted, and that the caller owns the target collection.
Vector gateopa.eval policy=kronos.vector.write pii_clean=true signed=true allow
- Store encrypted
Milvus holds ciphertext, not content
Vectors land in a tenant-scoped collection as ciphertext. An operator, an insider or an attacker with full database access gets data that is useless without your keys.
Store encryptedmilvus.upsert collection=kb_prod vectors=48,912 encrypted plaintext_at_rest=none
- Encrypted search
The query is encrypted too
Every query is encrypted before it leaves and matched against encrypted vectors. Results are decrypted only for the authorised user who asked. The database never sees plaintext.
Encrypted searchquery.encrypted matches=6 db_plaintext_exposure=none decrypt=authorised_user